Supply-chain posture without pip-and-pray: versioned images, CVE remediation, identity, audit, CUI, edge TLS, backup, and ops — inside the product, not beside it.
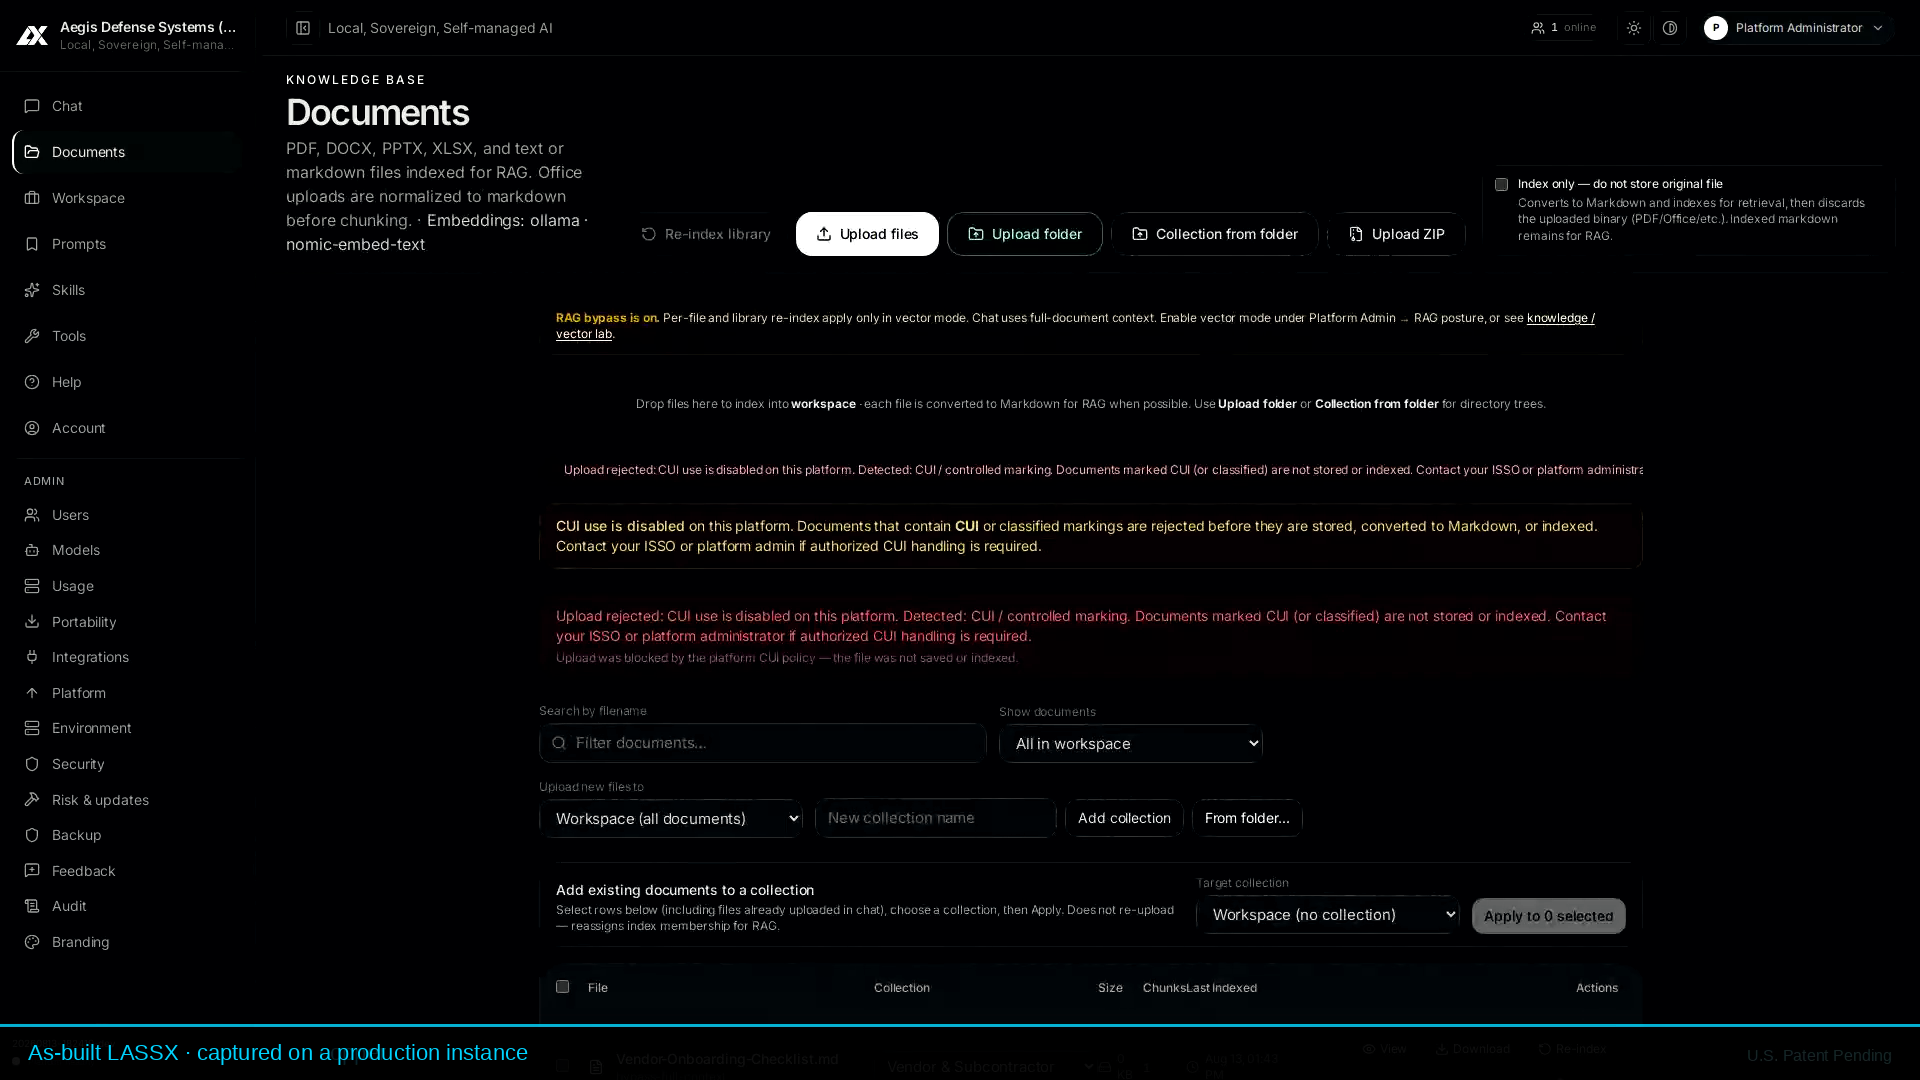
As-built LASSX · captured on a production instance — mock markings only — never real CUI. The public walkthrough is a labeled product preview.
supply chain
no pip-and-pray
CVE / SBOM
RBAC + IdP
audit
What you get
Appliance architecture: versioned compose images, no ad-hoc pip install
Built-in CVE/SBOM posture and remediation workflows
Policy and CUI controls at ingest and retrieval
Stakeholder takeaway
Prefer product controls and versioned media over ad-hoc host edits — those are supply-chain events, not harmless shortcuts.
Production LASSX capabilities described here run on customer-controlled appliances. This marketing site is a product preview — not a live Platform Admin or compliance assessment. No FedRAMP, CMMC, or HIPAA certification claims.