Built for operators who cannot outsource control
Share this URL with your ISSO / security reviewer.
LASSX is a self-managed AI platform you run on your own hardware. Knowledge, retrieval, and model choice stay under your authority — designed for federal contractors, healthcare, education, and other regulated environments.
Your hardware
Production runs as a controlled stack you host — no required public-cloud dependency.
Your knowledge
Corpus powers your retrieval. Not a multi-tenant SaaS training narrative.
Your authority
Policy-aware RAG, CUI-aware ingest, audit-friendly history under your governance.
Data boundary
Reference production topology. Components stay on infrastructure you operate.
Demo shell: Ask, Sources, Collections, History, Settings. Production adds Platform Admin and ops planes.
Retrieval orchestration, policy-aware composition, CUI ingest guards, audit events
Metadata, threads, and access control in Postgres; vectors in Qdrant on your hardware
Local or approved models under your policy — not a forced public copilot dependency
Platform operations
Production LASSX includes day-2 ops beyond chat and RAG. These are product capabilities on your appliance — not live consoles on this marketing demo host.
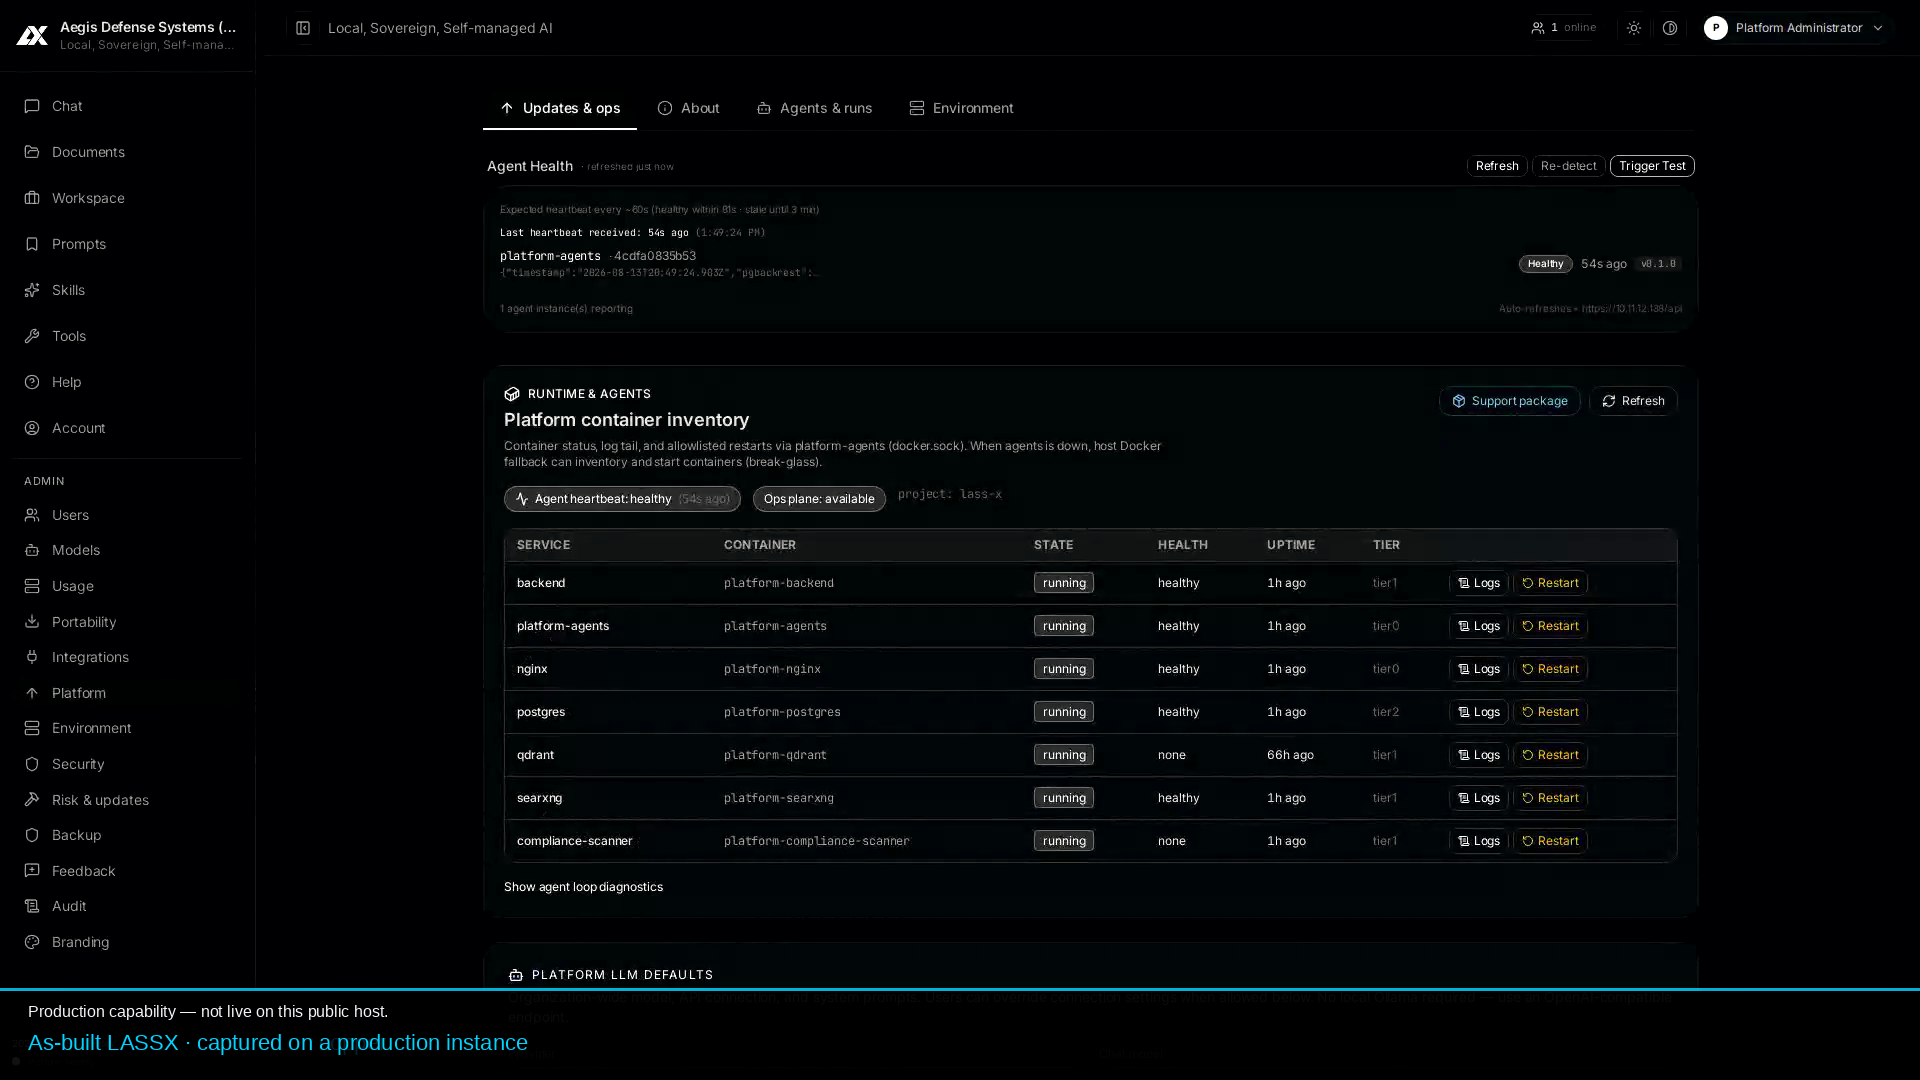
- Update Manager
Artifact-first upgrades for the controlled stack you host.
- Backup & restore
Backup targets and restore workflows defined per deploy.
- Enterprise identity
OIDC (and SAML path as product supports) for customer IdP — not wired on this public demo.
- OpenWebUI migration
Logical ETL cutovers from SQLite/Postgres OpenWebUI sources into LASSX.
- Compliance / assessor surfaces
Ops-oriented evidence and history for security review — capability intent, not a completed certification claim.
Data residency
Designed for single-machine and private-network deploy, including customer VPC and air-gap appliance options. Knowledge does not require a multi-tenant public store.
No training on your corpus
Customer documents power retrieval for the customer — not foundation-model training claims in the LASSX product story.
Audit-friendly history
Thread and operational history support review. Production posture emphasizes tamper-evident records for regulated ops.
CMMC foundation
Designed for CMMC-bound contractor environments and other regulated deployments. Custom regulated editions available — without overclaiming certifications you have not completed.
Encryption posture
Production posture supports encrypted volumes for data-at-rest, TLS for edge and service paths, and encrypted backup artifacts. Exact cipher suites and HSM/key custody are defined per customer deploy.
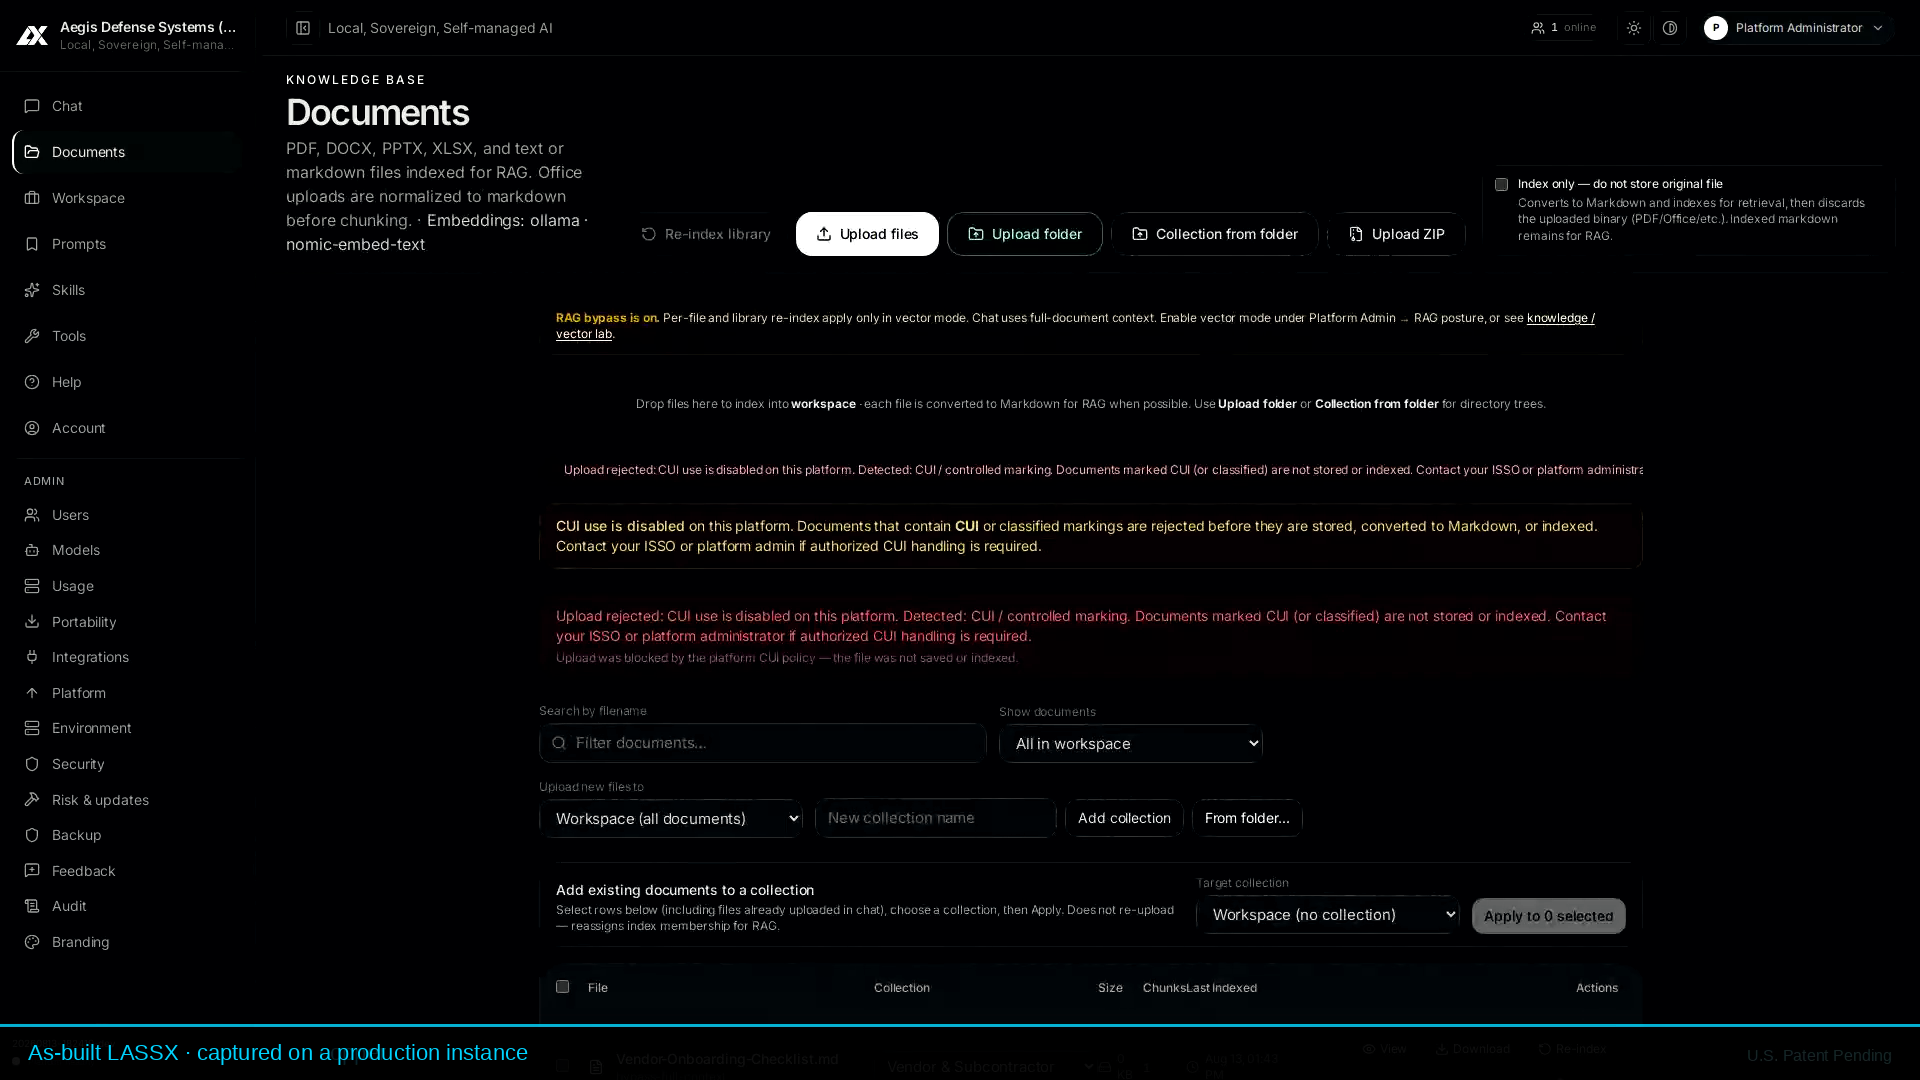
CUI-aware ingest policy
General knowledge indexing refuses documents marked CONTROLLED // CUI or otherwise detected as Controlled Unclassified Information. CUI belongs on an authorized enclave path with need-to-know and flow-down controls — not a mixed RAG index.
Shared-chat history can be limited to from-join (need-to-know). See chat collaboration.
Intellectual property
LASSX platform methods and architectures are U.S. Patent Pending. LASSX LLC retains all rights. Contact sales for IP discussion in the context of a pilot.
Pilot security
A typical pilot defines: data classes in scope, success criteria, who holds keys and admin access, retention for pilot artifacts, and an exit path. We do not ask you to send CUI into unmanaged cloud tools. Pilot environments should not host production CUI until an ATO/contract path is clear.
- Scope and environment under your control
- Clear allow/deny for sensitive data classes
- Security questionnaire available on request
sales@lassx.io · lassx.io
This page describes product intent and architecture posture. It is not a certification claim. Do not interpret language here as FedRAMP, CMMC assessment completion, HIPAA certification, or live private-cloud connectivity unless separately contracted and evidenced.